Aviation PKI: Certificate Management for Airside Devices, Radar Systems, and Ground Operations
Aviation PKI: certificate management for airside devices, radar systems and ground operations
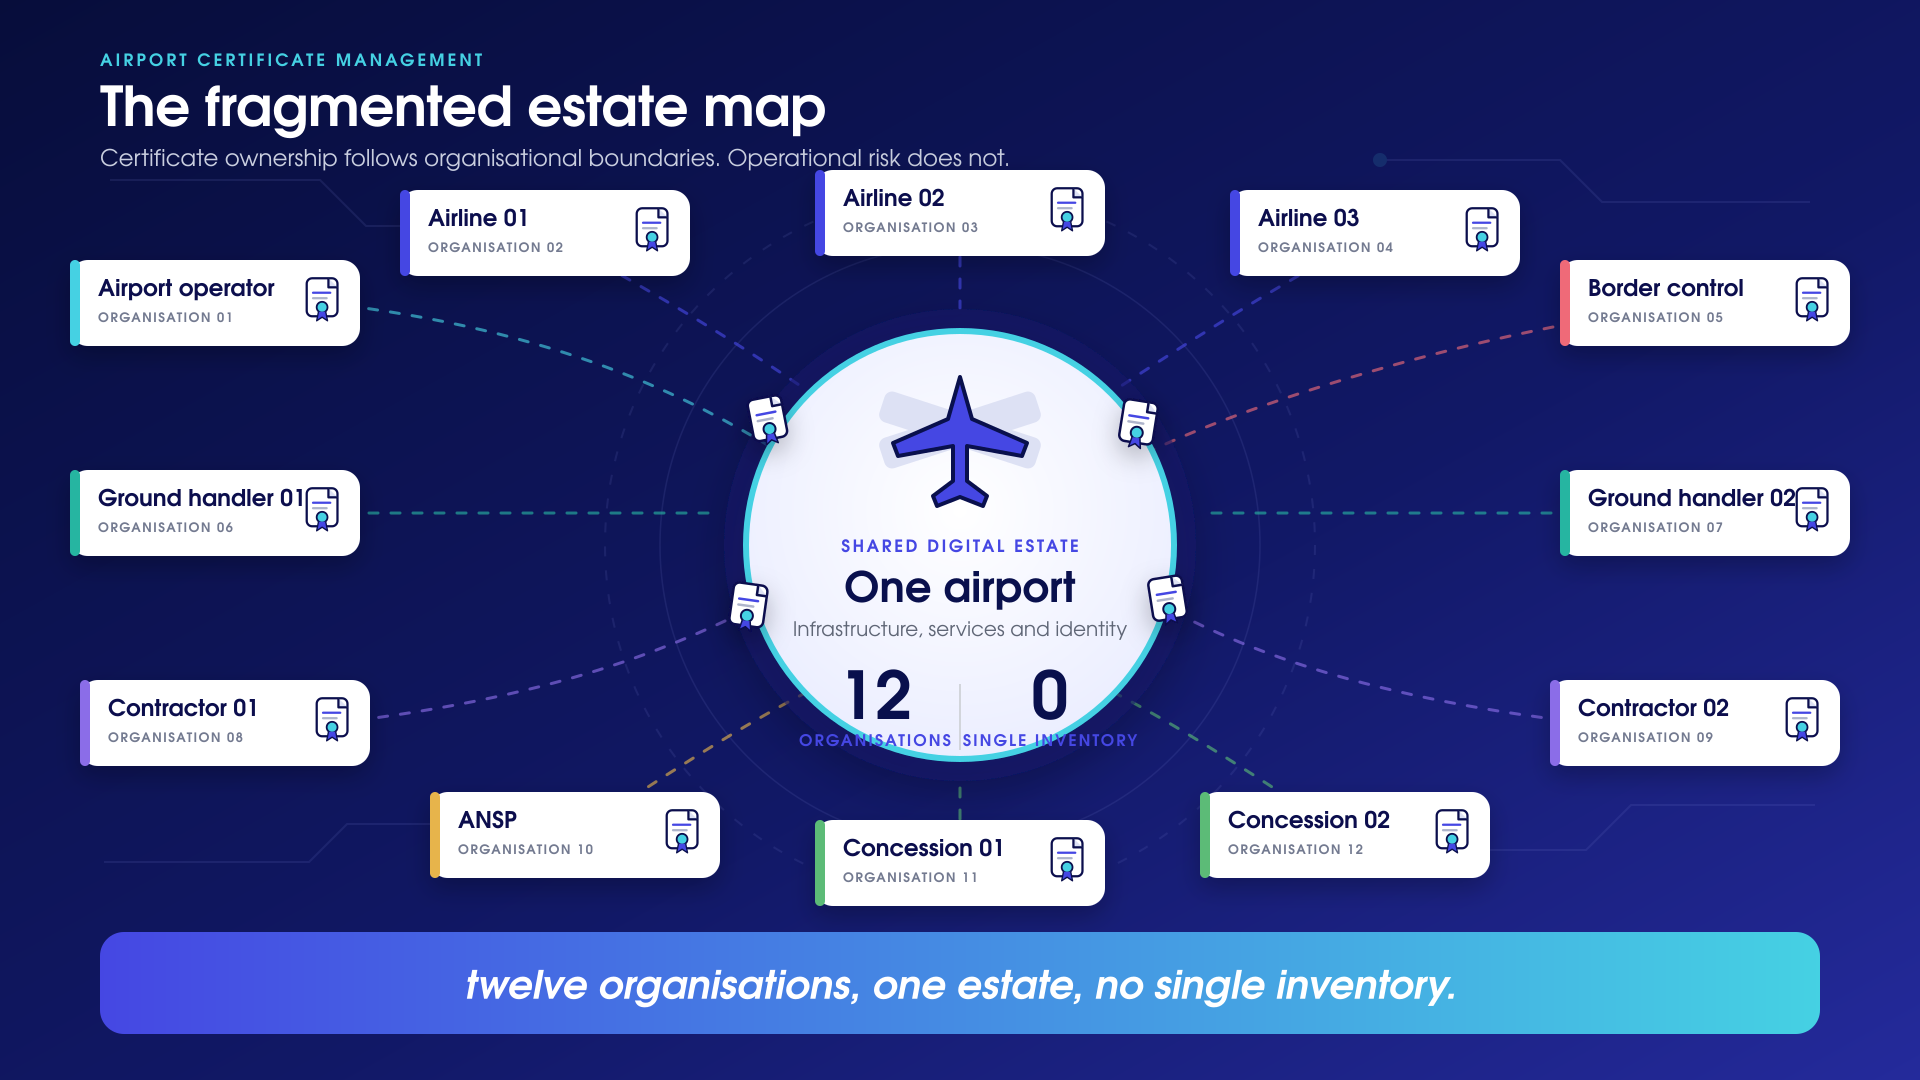
An airport is not one organisation. It is dozens.
The airport operator runs the terminal. Airlines run their own systems. Ground handlers, fuel providers, caterers, engineering contractors, border agencies, air navigation services and retail concessions all operate technology on or adjacent to the same estate. Each brings devices. Each brings certificates.
Almost nobody has a complete picture of them.
That is the practical starting point for aviation PKI. Not the cryptography, which is well understood, but the ownership question: who holds the inventory when the estate spans twelve organisations and none of them reports to the others.
Why certificates matter airside
Digital certificates underpin functions that aviation cannot run without:
- Ground-to-air and datalink communication, including ACARS and AeroMACS.
- Identity for airside handheld devices, mobile operational tools and engineering laptops.
- Signing and validation of electronic flight bag (EFB) content and maintenance software updates.
- Authentication between radar, navigation and surveillance platforms.
- Access control for restricted zones, including biometric and pass systems.
- Third-party and contractor access to operational networks.
- Protection of passenger and operational data in transit.
None of these are optional. All of them fail closed when a certificate expires, which is the correct security behaviour and the reason certificate management is an operational safety concern rather than an IT housekeeping task.
What goes wrong
Certificate failures in aviation do not stay contained. Airport operations are time-critical and tightly coupled, so a fault in one system propagates into others.
Typical consequences:
- Flight information displays or gate management systems drop out, with immediate passenger impact.
- Airside access control fails, creating queues at security checkpoints and staff gates.
- Handheld devices lose connection to operational systems, forcing manual fallback for turnaround, baggage or de-icing.
- Engineering or maintenance tools cannot authenticate, delaying aircraft release to service.
- Audit and investigation are compromised, because logs cannot be attributed to a verified identity.
- Weak or expired certificates create an opening for an attacker already inside the perimeter.
A single certificate on a single system can push an airport into manual operation at its busiest hour. The cost is measured in delayed rotations and missed slots, not in the price of the certificate.
Four things that make aviation harder than most sectors
Generic certificate advice does not survive contact with an airside environment. Four constraints change the problem.
1. The estate is shared, not owned
Certificates are issued by airlines, installed by suppliers, embedded by device manufacturers and renewed by contractors. Responsibility is distributed and frequently assumed rather than assigned. When something expires, the first question is usually whose certificate it was.
2. Change control is a safety process
On a corporate network, a certificate renewal is a low-risk change. On a system in scope of a safety case, the same renewal may require impact assessment, regression testing and a scheduled change window. That is appropriate. It is also slow, and it does not scale well against shortening certificate lifetimes.
3. Assets stay in service for decades
Airside hardware, surveillance systems and navigation equipment are specified on ten to twenty year horizons. Cryptography embedded at procurement is still running long after the algorithm choices have aged. Some devices cannot support modern protocols at all, and cannot be replaced on a security timescale.
4. Revocation checking is unreliable in segregated networks
Operational networks are deliberately segmented, and often have no route to a public OCSP responder or CRL distribution point. Certificate validation that works in a test environment can behave very differently on an airside VLAN.
The Fragmented Estate Map
The 47-day problem
Public TLS certificate lifetimes are falling to 47 days.
For passenger-facing services — booking, check-in, airport websites, APIs to airline systems — this is a straightforward automation problem with a well-understood answer.
For operational technology it is harder. A renewal cycle that was annual, and could be absorbed within existing change processes, becomes roughly eight cycles a year on every affected system. Where each renewal carries a change control burden, that arithmetic does not work. The only sustainable answers are automation for the systems that can take it, and private PKI with appropriate lifetimes for the systems that cannot.
Deciding which is which requires an inventory. Most airports do not have one.
What certificate lifecycle management provides
Certificate Lifecycle Management gives aviation organisations a single operating model across a fragmented estate.
In practice:
- Discovery. A complete inventory across IT, cloud and operational technology, including certificates installed by suppliers and never recorded.
- Ownership. A named owner for every certificate, and an escalation route when that person leaves or the contract ends.
- Automated renewal and revocation for systems that support it, removing the manual step most likely to fail.
- Monitoring for weak algorithms, short keys, misconfigured chains and approaching expiry, with enough lead time to work within change control.
- Policy enforcement applied consistently regardless of which organisation requested the certificate.
- Integration with identity, access and device management, so airside credentials and system certificates are governed together.
The outcome is that renewals become predictable and scheduled rather than discovered at the point of failure.
Where the dependency sits
Certificate dependency in an airport is broader than most operators expect. It typically includes:
- Airside handheld devices and mobile operational tools.
- Radar, navigation and surveillance communication platforms.
- Security, biometric and access control systems.
- Airline and ground handler maintenance and engineering software.
- Baggage handling, passenger flow and stand allocation systems.
- Building management, CCTV and environmental systems on the operational network.
- Vendor remote-access and support tunnels.
That last item is worth particular attention. Third-party access and device trust in multi-vendor supply chains is where the governance gap is usually widest.
Regulatory context
Certificate management increasingly appears inside compliance obligations rather than alongside them.
- UK aviation operators designated under the NIS Regulations are assessed against the NCSC Cyber Assessment Framework, which covers identity, access control and system security.
- The CAA's cyber security oversight process applies to organisations in scope, with assurance activity against defined outcomes.
- EASA Part-IS introduces information security management requirements for organisations under EU aviation regulation, with certificate and key management falling within scope.
- Airworthiness security guidance, including DO-326A and ED-202A, addresses security in the design and continued airworthiness of aircraft systems.
Demonstrating control over cryptographic assets is difficult without an inventory and an audit trail. CLM produces both as a by-product of normal operation.
Verify current applicability and dates against your own regulatory position.
Looking further ahead
Aviation's long asset lifecycles make post-quantum readiness an unusually early concern.
Equipment being specified now will still be in service when today's public-key algorithms are no longer considered safe. Systems handling data with a long confidentiality requirement are exposed to harvest-now-decrypt-later collection today, regardless of when a cryptographically relevant quantum computer arrives.
The practical response is not to replace algorithms now. It is to know what you have and to build the capability to change it:
- Establish a cryptographic inventory covering algorithms, key lengths and protocols, not just certificate expiry dates.
- Add crypto-agility requirements to procurement, so new airside equipment can be updated in the field.
- Identify systems that cannot be updated, and plan their replacement on an asset refresh cycle rather than an emergency one.
Crypto-agility is what turns the next cryptographic change into a managed programme rather than a fleet-wide rebuild.
What Unsung does
We are vendor-neutral, and we work on PKI exclusively.
With aviation clients that typically means:
- Discovery across the full estate, including operational technology and supplier-installed certificates that sit outside any central record.
- Designing PKI and CLM architectures appropriate to segregated operational networks, including private trust hierarchies where public certificates are not viable.
- Integrating certificate operations with airside identity, access and device management.
- Establishing governance that works across airport operators, airlines, ground handlers and contractors, with ownership defined rather than assumed.
- Post-quantum planning, from cryptographic inventory through to procurement requirements and migration sequencing.
The objective is a trust model that holds across every organisation operating on the estate, not just the one that commissioned the work.
A PKI Health Check is usually where this starts. It establishes what is actually deployed, what is at risk and what needs attention first.
Frequently Asked Questions
Why is PKI important for aviation operations?
What are the risks of poor certificate management in aviation?
What aviation systems require certificate lifecycle management?
What benefits does PKI implementation provide for airports?